Mimecast was founded in London in 2003 by South African entrepreneurs Peter Bauer and Neil Murray, who built a cloud-based company just as business communications shifted online. From its inception protecting email as organisations moved to the cloud, the company now finds itself at another inflection point with agentic AI.
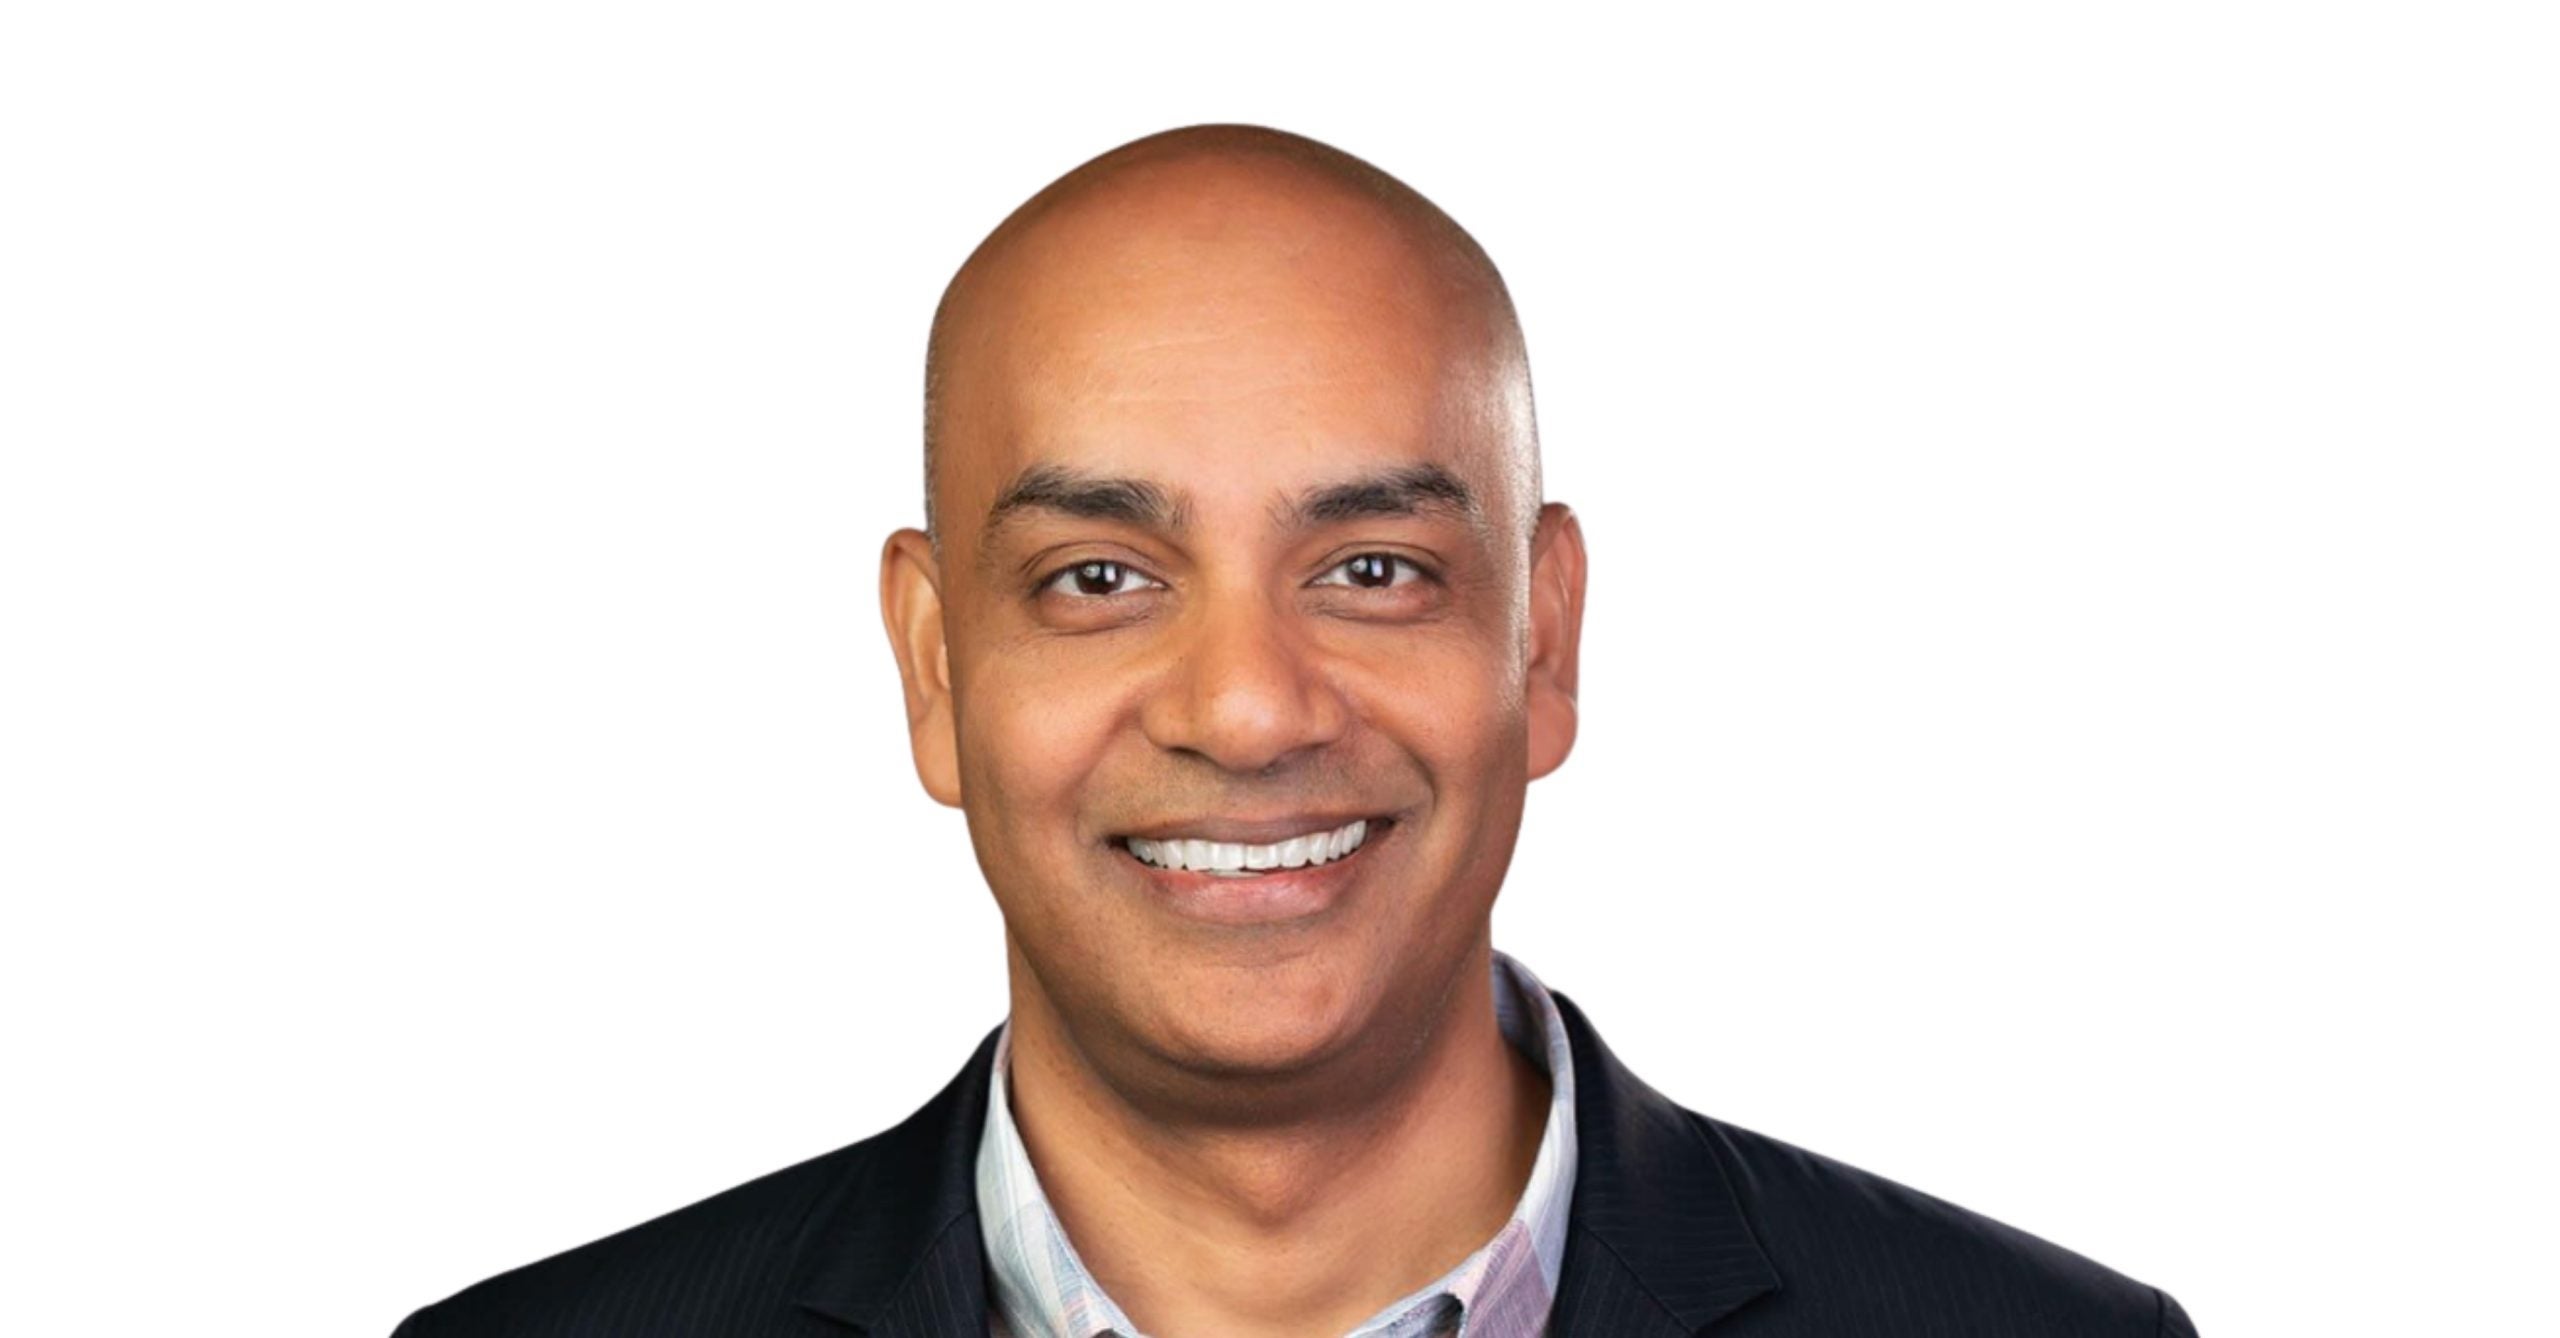
Ranjan Singh became Mimecast’s CEO in June after joining the company as chief product and technology officer in April 2025. With the company’s US headquarters in Lexington Massachusetts, its global headquarters in London and Singh residing in New York, he jokes that his office is essentially a seat on United Airlines.
Go deeper with GlobalData
Access deeper industry intelligence
Experience unmatched clarity with a single platform that combines unique data, AI, and human expertise.
But in the age of remote working, managing a company with a hybrid and globally disparate workforce is the least of his concerns. What really keeps him up at night is the next generation of cyber threat being unleashed by agentic AI.
The following conversation has been edited for clarity and length.
Lara Williams: How has Mimecast’s mission changed in today’s AI era from the old days of protecting customers in the cloud?
Ranjan Singh: Historically, most risks were tied to users. If you think about it, a user is the one who gets compromised 90% of the time. With AI, I still think that same 90% still applies; the difference is that user threats are now extended by AI, rather than replaced by a totally new threat.
Users are giving AI agents permissions to do all kinds of things such as “Read my email”, “Send email on my behalf”. I might have 20 plus agents running on my desktop. So, user risks are really extended in the age of AI, and that is how we have to think about it.
From a pivoting standpoint, customers are first asking, do I know where my AI is? Even customers that have rolled out AI responsibly, with good governance practices and policies, are constantly discovering more AI use and shadow AI use in their environments.
From a cyber security standpoint, the pivot is from understanding your user risks to also understanding where your AI risks are. So step on is before you can protect something, you have to understand where the risk lies and what the shadow AI environment looks like.
The second pivot is operating at the speed of AI. An agent can read an email faster and take actions faster than a human. If a threatening email or message lands and you have given agents permissions, they can act a lot faster than a user. So all of us in the world of cyber security are asking how we move at the speed of AI to tackle these challenges? And that’s really the big challenge.
LW: Essentially, what you describe is still all user risk, even though it’s in the context of AI and shadow AI? What has actually changed in terms of risk?
RS: What has changed, Lara, is the range and sophistication of threat vectors aimed at users: email, phishing, collaboration channels, deepfake videos, SMS text messages.
The first change is the quality of phishing. It has become very sophisticated. Humans used to be able to distinguish some kind of an attack from phishing, vishing or smishing attacks relatively easily. Now they can be indistinguishable from legitimate communications. You really need technology to help uncover them, and training and education to support that.
The second change is human behaviour. If you get prompted 15 times a day by Claude, say, an AI assistant asking, “Do you want to take this action? Allow once or always allow?”, the natural instinct is to say, “I am bored of clicking this; I will just always allow.” What you may not understand is what access you have just given that agent.
We have all heard scenarios where, as they say, water finds its way; well, an agent finds its way, no matter how many guardrails you put in place. So, hence the ability to now be able to surface what agents are allowed to do, and surface that across all the places a user operates: endpoint, browser, mobile phone.
You need to understand what access the user has, and what access the user has given to the agent. That is really the starting point.
LW: On moving at the speed of AI. Is user education keeping pace? When we talk about permissions, it sounds like educating the user is critical.
RS: Educating the user is one important dimension. Is it moving at the pace of AI? In select circles, it is.
You cannot run the same generic phishing simulation and training for everyone. With AI, we have the opportunity to learn what Lara does on a daily basis, for example, what business she is in, what function she is in; what I do, what my role is, and so on. Using AI, you can customise training and phishing simulations, to drive the right user behaviours and help people learn.
You can also use AI when a user takes a risky or unsanctioned action, you can nudge them. And you can customise. I think of it as “customisation of one”: you can truly understand individual user behaviour and the AI behaviour that the user has enabled, and then drive customised actions, both from a coaching and teaching perspective and from a risk reduction, blocking and protection perspective.
LW: Without citing names, what is the biggest mistake you have seen customers make in recent months?
RS: I would point out two things.
First, you can never build enough coaching and training around users, because in the age of AI the user is overwhelmed. We might think we are getting fewer emails, but in reality more people are sending more AI generated emails and documents. A user is therefore more likely to make a mistake.
You cannot assume that coaching and training alone are enough. You have to assume the likelihood of mistakes is high. Someone in my role, for example, might be processing a hundred purchase orders or invoices a month. If I do not read every DocuSign carefully before I sign off, there is a significant risk.
Second, many customers—and CISOs in particular—do not spend enough time surfacing the risk. There is often a posture of “I have it covered; I have blocked all these tools”. But in this day and age users are curious; they want to try the latest and greatest technology. If you rely on blocking and restrict user freedom, users are more likely to go and find workarounds to use those tools. Those are the things we have observed.
You mentioned permissions and autonomy. There is blocking user permissions, but when it comes to AI agents, what level of autonomy is sensible? How do you evaluate how much autonomy to give agents versus humans?
A good starting point is that an agent should never have more autonomy than the user. If companies find themselves in that inverse situation, I would be looking at that very closely and trying to close that gap.
User freedom is generally already defined in most organisations. They have policies ranging from conservative to more aggressive, depending on line of business and region. In the agentic world, you can think about it similarly: start with what is safe.
A simple example: agents can read Slack or Teams channels and emails, but do not have write access or cannot generate responses. That is a good starting point to understand how the world is operating in their environment.
A critical aspect is that you must know what is going on in your environment. You need tools and software in place that give you that understanding. Under a user’s identity and single sign on, you might have granted some agents permissions to do a set of things—whether those are cloud agents, copilots or agents embedded in Microsoft Excel or Word.
As long as you understand what is happening and can discover and identify those situations, I think there can be a gradual expansion of both user and AI autonomy. If you don’t have systems in place to uncover what is happening—not just from a single sign on authorisation standpoint, but also by actually observing activity on the surfaces—you are at risk.
You should not assume that because you have given permissions to five agents, you will only find five. You should assume that, if users have the ability, they will go to websites, use tools like DeepSeek or the latest models, download things and experimenting. You need tools to uncover all agentic activity, tie it back to the user and then decide what to allow or block, following the simple rule that an agent should not have more autonomy than a user.
Do you think current observability tools are effective enough to identify rogue AI agents? What is your advice to technology leaders in big enterprises dealing with this?
First, it is a very tough environment for CISOs today. There are more AI security tool providers than you can shake a leg at. You are not going to test every tool or believe every claim.
Some CISOs are taking a “wait and see” approach, watching to see what surfaces. Many are instead going back to their core existing platform providers and asking them for solutions and advice. We see more and more of that trend.
So you go to your endpoint security provider, your network security provider, your email or human risk security provider, and say: “What do you have in place that can help me uncover these risks?” That is typically the approach.
In terms of toolsets, it is a fast evolving space. Many software tools will claim they can deliver discoverability and observability. CISOs and their teams themselves should evaluate those tools themselves rather than simply believe the claims.
Equally important is not just observing and identifying, it’s can you take governance actions? Can you take blocking actions? And, most importantly, if there is some kind of an event, can you retrace what happened?
Any tool, set of tools or platform provider has to help you do all of these things. No tool is perfect, so you should assume that some kind of event will occur. The key questions then are: can you identify what happened, and can you retrace it so that you can put better blocking and protection mechanisms in place?
LW: If you were a CISO, where would you draw the line? What would you refuse to let an AI agent do, even if the business was pushing for maximum automation?
As a starting point, I would limit right access across many tools. For example, do not let AI write emails on your behalf, or write messages on your behalf, without very strong controls.
Right actions are where you can influence outcomes, so they should be treated very carefully. Agents reading from software and performing analysis is one thing, unconstrained right actions can be extremely harmful.
I would also look very closely at autonomous AI agents operating as service accounts, taking actions independently of users. You need strong guardrails there. We know guardrails do not always work, but there should be a lot of focus and activity because those agents are hard to identify. They are not tied to a specific user or clear entity; they are independent non human identities.
LW: Has the current threat environment changed the CISO–CEO relationship? How do you see that relationship evolving?
It is certainly more top of mind. CISOs and CEOs—and, for that matter, CIOs and chief transformation officers—are working together, probably more closely than ever.
CEOs, regardless of ownership structure (whether private equity backed or public), are expected to leverage AI to drive productivity, efficiency and innovation. So, there is pressure on that side.
From the CISO, legal and compliance standpoint, there is pressure to do this safely and compliantly, while still protecting user freedom. These three roles are spending more and more time together, trying to figure out how to drive transformation, innovation and operational efficiency in a highly secure way. They have probably come closer than ever before, and that is certainly true at Mimecast.